Master Kubectl Port-Forwarding: Ultimate Guide for Effortless Container Management


Introduction
In the world of container management, Kubernetes (k8s) has become the de facto standard for orchestrating containers. One of the essential tools in a Kubernetes administrator's toolkit is kubectl, which allows you to interact with your cluster using command-line tools. Port-forwarding is a feature of kubectl that enables you to forward ports from your local machine to a pod in a Kubernetes cluster. This guide will delve into the intricacies of using kubectl port-forwarding for effortless container management.
Understanding Kubernetes Port-Forwarding
Port-forwarding in Kubernetes is a feature that allows you to redirect network traffic from your local machine to a pod within your cluster. This is particularly useful when you need to access services running inside a pod from your local machine. For example, you might want to access a database or a web application running inside a pod.
Key Concepts
- Pods: The smallest deployable unit in Kubernetes. A pod can contain one or more containers.
- Ports: The endpoints for communication within a container or pod.
- Local Port: A port on your local machine that is being redirected to a port in the pod.
- Container Port: A port within the container that is being exposed.
Why Use Port-Forwarding?
- Debugging: Access services inside a pod for debugging purposes.
- Development: Test applications running in the cluster from your local machine.
- Monitoring: Monitor the health of services running inside a pod.
Getting Started with kubectl port-forward
To use kubectl port-forward, you need to have kubectl installed and configured to communicate with your Kubernetes cluster. Once you have that set up, you can start using port-forwarding.
Basic Syntax
The basic syntax for kubectl port-forward is as follows:
kubectl port-forward [POD_NAME] --local=[LOCAL_PORT]:[CONTAINER_PORT]
[POD_NAME]: The name of the pod you want to forward traffic to.[LOCAL_PORT]: The port on your local machine that you want to use.[CONTAINER_PORT]: The port in the container that you want to expose on your local machine.
Example
Let's say you have a pod running a web server on port 8080. You want to access it from your local machine on port 80. You would use the following command:
kubectl port-forward my-web-server-pod 80:8080
This command would forward traffic from your local port 80 to the web server's port 8080 inside the pod.
APIPark is a high-performance AI gateway that allows you to securely access the most comprehensive LLM APIs globally on the APIPark platform, including OpenAI, Anthropic, Mistral, Llama2, Google Gemini, and more.Try APIPark now! 👇👇👇
Advanced Usage of kubectl port-forward
Multiple Ports
You can forward multiple ports using the following syntax:
kubectl port-forward [POD_NAME] --local=[LOCAL_PORT1]:[CONTAINER_PORT1] --local=[LOCAL_PORT2]:[CONTAINER_PORT2]
This command would forward both ports 80 and 8080 from your local machine to the corresponding ports in the pod.
Using a Specific Container
If your pod contains multiple containers, you can specify which container's port you want to forward using the --container flag:
kubectl port-forward [POD_NAME] --container=[CONTAINER_NAME] --local=[LOCAL_PORT]:[CONTAINER_PORT]
Using a Service
You can also forward traffic to a service instead of a pod:
kubectl port-forward [SERVICE_NAME] --local=[LOCAL_PORT]:[SERVICE_PORT]
This command would forward traffic to the service's port from your local machine.
Forwarding to a NodePort
If your service is exposed using NodePort, you can forward the traffic to your local machine using the following command:
kubectl port-forward [POD_NAME] --node=[NODE_NAME] --local=[LOCAL_PORT]:[NODE_PORT]
Troubleshooting Common Issues
Connection Refused
If you encounter a "connection refused" error, it could be due to one of the following reasons:
- The pod is not running.
- The container is not listening on the specified port.
- There is a firewall blocking the connection.
Timeout Errors
Timeout errors can occur if:
- The network connection is slow.
- The pod is taking too long to start.
- The container is not responding to requests.
APIPark Integration with kubectl port-forward
Integrating APIPark with kubectl port-forward can enhance your container management experience. APIPark, an open-source AI gateway and API management platform, provides several benefits for Kubernetes administrators:
- Easy API Management: APIPark allows you to manage and monitor APIs running in your cluster, making it easier to troubleshoot and optimize your applications.
- Enhanced Security: APIPark can help secure your containerized applications by providing authentication, authorization, and rate limiting.
- Performance Monitoring: APIPark offers performance monitoring capabilities that can help you identify bottlenecks and optimize your containerized applications.
To integrate APIPark with kubectl port-forward, you can use the APIPark API to retrieve and manage API configurations for your services. This can be done using the following command:
kubectl port-forward my-api-service --container=api-container --local=[LOCAL_PORT]:[API_PORT] --insecure-skip-tls-verify
This command forwards traffic from your local machine to the API container's port within the pod, using the APIPark API for configuration management.
Conclusion
Kubectl port-forwarding is a powerful feature that simplifies container management in Kubernetes. By understanding the basics and advanced usage of port-forwarding, you can efficiently manage your containers and troubleshoot issues as they arise. Integrating APIPark with kubectl port-forward can further enhance your container management experience by providing advanced API management and security features.
FAQs
1. What is Kubernetes port-forwarding? Kubernetes port-forwarding is a feature that allows you to redirect network traffic from your local machine to a pod within your Kubernetes cluster. It is useful for debugging, testing, and monitoring applications running inside pods.
2. Can I forward multiple ports using kubectl port-forward? Yes, you can forward multiple ports using the --local flag multiple times in the kubectl port-forward command.
3. How do I specify a container when using kubectl port-forward? You can specify a container using the --container flag followed by the name of the container you want to forward traffic to.
4. Can I forward traffic to a service instead of a pod? Yes, you can forward traffic to a service using the kubectl port-forward command by specifying the service name instead of the pod name.
5. What is APIPark and how does it integrate with kubectl port-forward? APIPark is an open-source AI gateway and API management platform that can be integrated with kubectl port-forward to provide advanced API management, security, and performance monitoring features for containerized applications.
🚀You can securely and efficiently call the OpenAI API on APIPark in just two steps:
Step 1: Deploy the APIPark AI gateway in 5 minutes.
APIPark is developed based on Golang, offering strong product performance and low development and maintenance costs. You can deploy APIPark with a single command line.
curl -sSO https://download.apipark.com/install/quick-start.sh; bash quick-start.sh
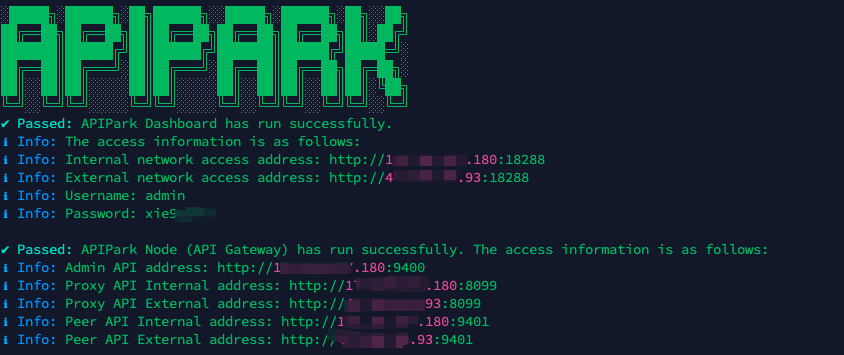
In my experience, you can see the successful deployment interface within 5 to 10 minutes. Then, you can log in to APIPark using your account.
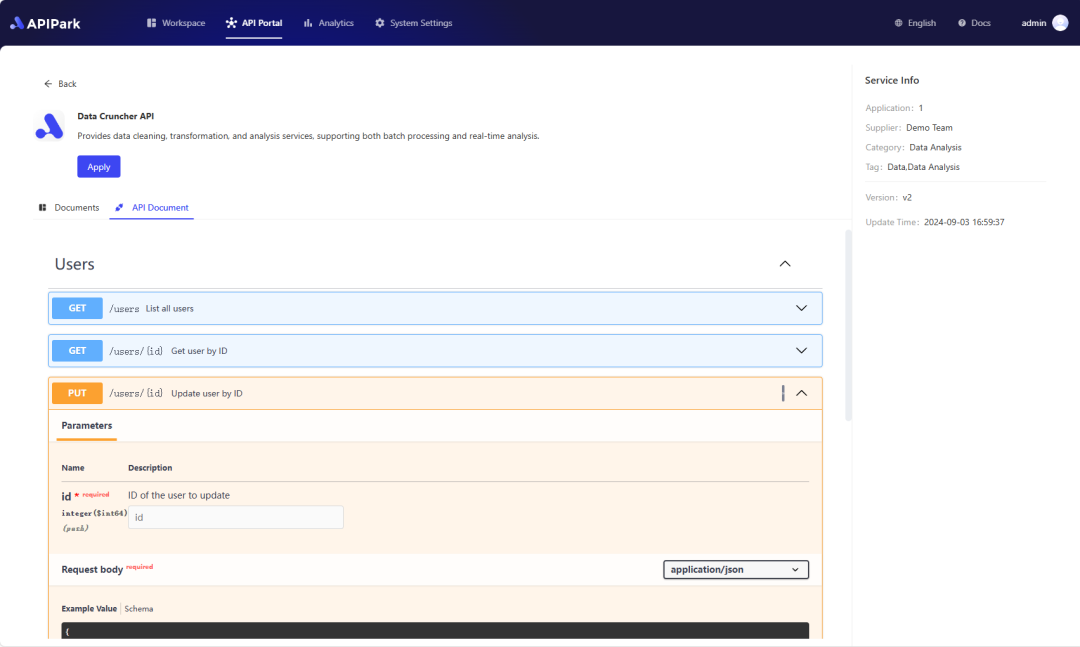
Step 2: Call the OpenAI API.